#threatintel
314 posts · Last used 2d
Boosted by @welcome@friends.deko.cloud
Hi Infosec.Exchange. I'm Ilja Krasnjanski, an independent security researcher.
This year I reconstructed UNK_DeadDrop, a fake-job-interview campaign aimed at developers, from retained artifacts without running a sample: a 14-part series, a paper, and an open-source static scanner with YARA rules. I'll post the findings here one at a time.
https://krasforge.github.io/UNK_DeadDrop/
#introduction #infosec #ThreatIntel #malware
Boosted by @welcome@friends.deko.cloud
Hi everyone! 👋 I'm Kushal, a cybersecurity student working toward a SOC analyst role.
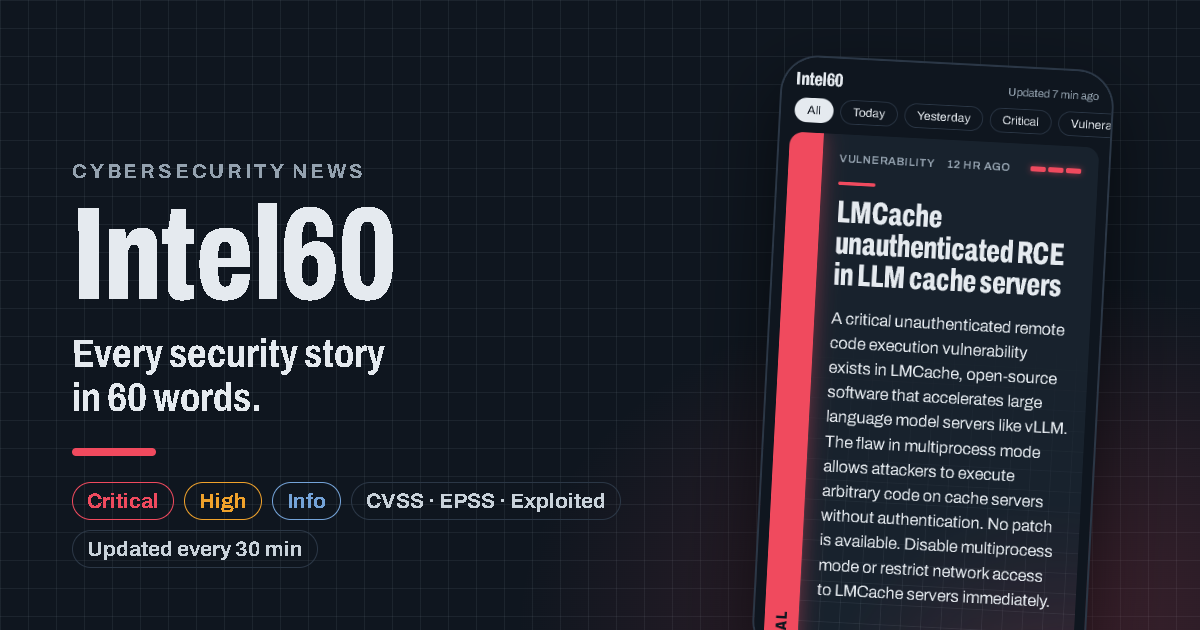
I built Intel60 (https://intel60.app) every 30 min it turns news from 8 security outlets + CISA KEV into 60-word, severity-rated briefs with CVSS, EPSS and "actively exploited" tags. Free, no sign-up, no ads.
Here to learn from the blue team community. Feedback very welcome!
#introduction #infosec #cybersecurity #blueteam #threatintel #SOC
What detection format would you like to have if you got detections online? (e.g. for a recent attack/vuln wave like php2shell)
#dfir #infosec #cybersecurity #askfedi #incidentresponse #osint #threatintel #threatintelligence #opensourceintelligence
What detection format would you like to have if you got detections online? (e.g. for a recent attack/vuln wave like php2shell) #dfir #infosec #cybersecurity #askfedi #incidentresponse #osint #threatintel #threatintelligence #opensourceintelligence
Sigma 32%
Just gimme hashes and IPs 20%
Yara 24%
KQL 20%
Other (please specify) 4%
13 people · Closed
Boosted by @Ichinin@infosec.exchange
Symantec: APT28 (GRU Unit 26165) Targets Defense Firms in Two NATO Countries
https://www.security.com/threat-intelligence/swallowtail-russia-nato-targets
#threatintel #Russia #cyberespionage #IOC
Boosted by @oxy@social.bsdlab.au
Dear threat actors, please be more creative with your UI like this one plz...
Sincerely me
#cybersecurity #threatintel
New configuration detected for DDosia. Hosts:
(truesec.com) Denmark Raises Threat Level for Destructive Cyberattacks Amid Escalating Russian Hybrid Warfare
In brief - This article discusses the increased risk of destructive cyberattacks in Denmark and Europe, driven by Russian hybrid warfare aimed at pressuring nations to reduce support for Ukraine.
Technically - This article categorizes the threat landscape into cybercrime, espionage, and cyber warfare, noting that while crime remains the most common threat, Russian state-sponsored activity is escalating. Technical vectors identified include Distributed Denial of Service (DDoS) attacks, the compromise of CCTV systems, and the manipulation of unprotected critical infrastructure components. Furthermore, the report highlights the use of proxy or disposable agents to target defense sector supply chains, factories, and warehouses through destructive cyber operations.
Source: https://www.truesec.com/hub/blog/danish-intelligence-services-raises-threat-for-destructive-cyberattacks
#ThreatIntelligence #ThreatIntel #Cybersecurity #Infosec
The kiddies have their modern shell shock and the scans are underway. Hope you patched.
85 11 187 35 - attacker
31 56 197 72 - payload staging
#threatintel#citrix#pitboss
Quiz time: which of these domains is impersonating Apple?
quizearny[.]shop, rewardquiz[.]org look like generic quiz sites. applerewards[.]net is more obvious. All of them belong to a cluster serving identical Apple impersonation content, prompting victims to claim an Apple gift card reward by handing over their personal details. testar[.]ink, "to test", was the first to be created, nearly a month before the others went live, which may say something about how this campaign got started.
What makes this cluster more interesting is what happens after you click the "Claim Your Apple Reward" button on the initial page. Different locations, different device types, different destinations. Classic TDS.
This cluster is a good reminder that brand impersonation lives in the page content, not just the domain name. A quiz site with no Apple in its name can be just as dangerous as an obvious lookalike.
#dns #threatintel #threatintelligence #cybercrime #cybersecurity #infosec #infoblox #infobloxthreatintel #axur #lookalike #scam #tds
validx[.]shop looked fine at first glance. "Normal" name servers, a real mail setup, nothing that immediately stood out at the apex level. One subdomain didn't quite fit, though. It was getting DNS queries that were absurdly long and frequent for a new domain that nobody was really visiting. Rather than that being web traffic, we detected it as likely tunneling.
Turns out it wasn't a one-off. The same setup shows up on hundreds of other domains.
The domain names follow a similar pattern: short, brandable and portmanteau-y (i.e., cordkit, zenithly, queuebox), spread across a long list of cheap gTLDs with the same registrar.
The tunnel itself is answering with TXT records like:
⚠️ "H2;n=5;k=3;ol=2004;sz=800;cz=gz"
As best as we can tell, that's a shard count, a reconstruction threshold, a length, a chunk size, and a compression flag. We checked the signature against a number of known DNS tunnelling tools and none of them write a header like this.
We watched two more domains get registered mid-investigation, hours apart, which was fun to see and immediately block
We've got the infrastructure and the method. We haven't got a payload, and we haven't matched this header format to anything documented publicly.
Has anyone else run into this, recognize the TXT format above, or have a sample of a possible malware source? We'd like to hear from you.
⛔ validx[.]shop
⛔ cordkit[.]online
⛔ zenithly[.]best
☠️ 95[.]179[.]159[.]229
#dns #threatintel #threatintelligence #cybercrime #cybersecurity #infosec #infoblox #infobloxthreatintel #c2
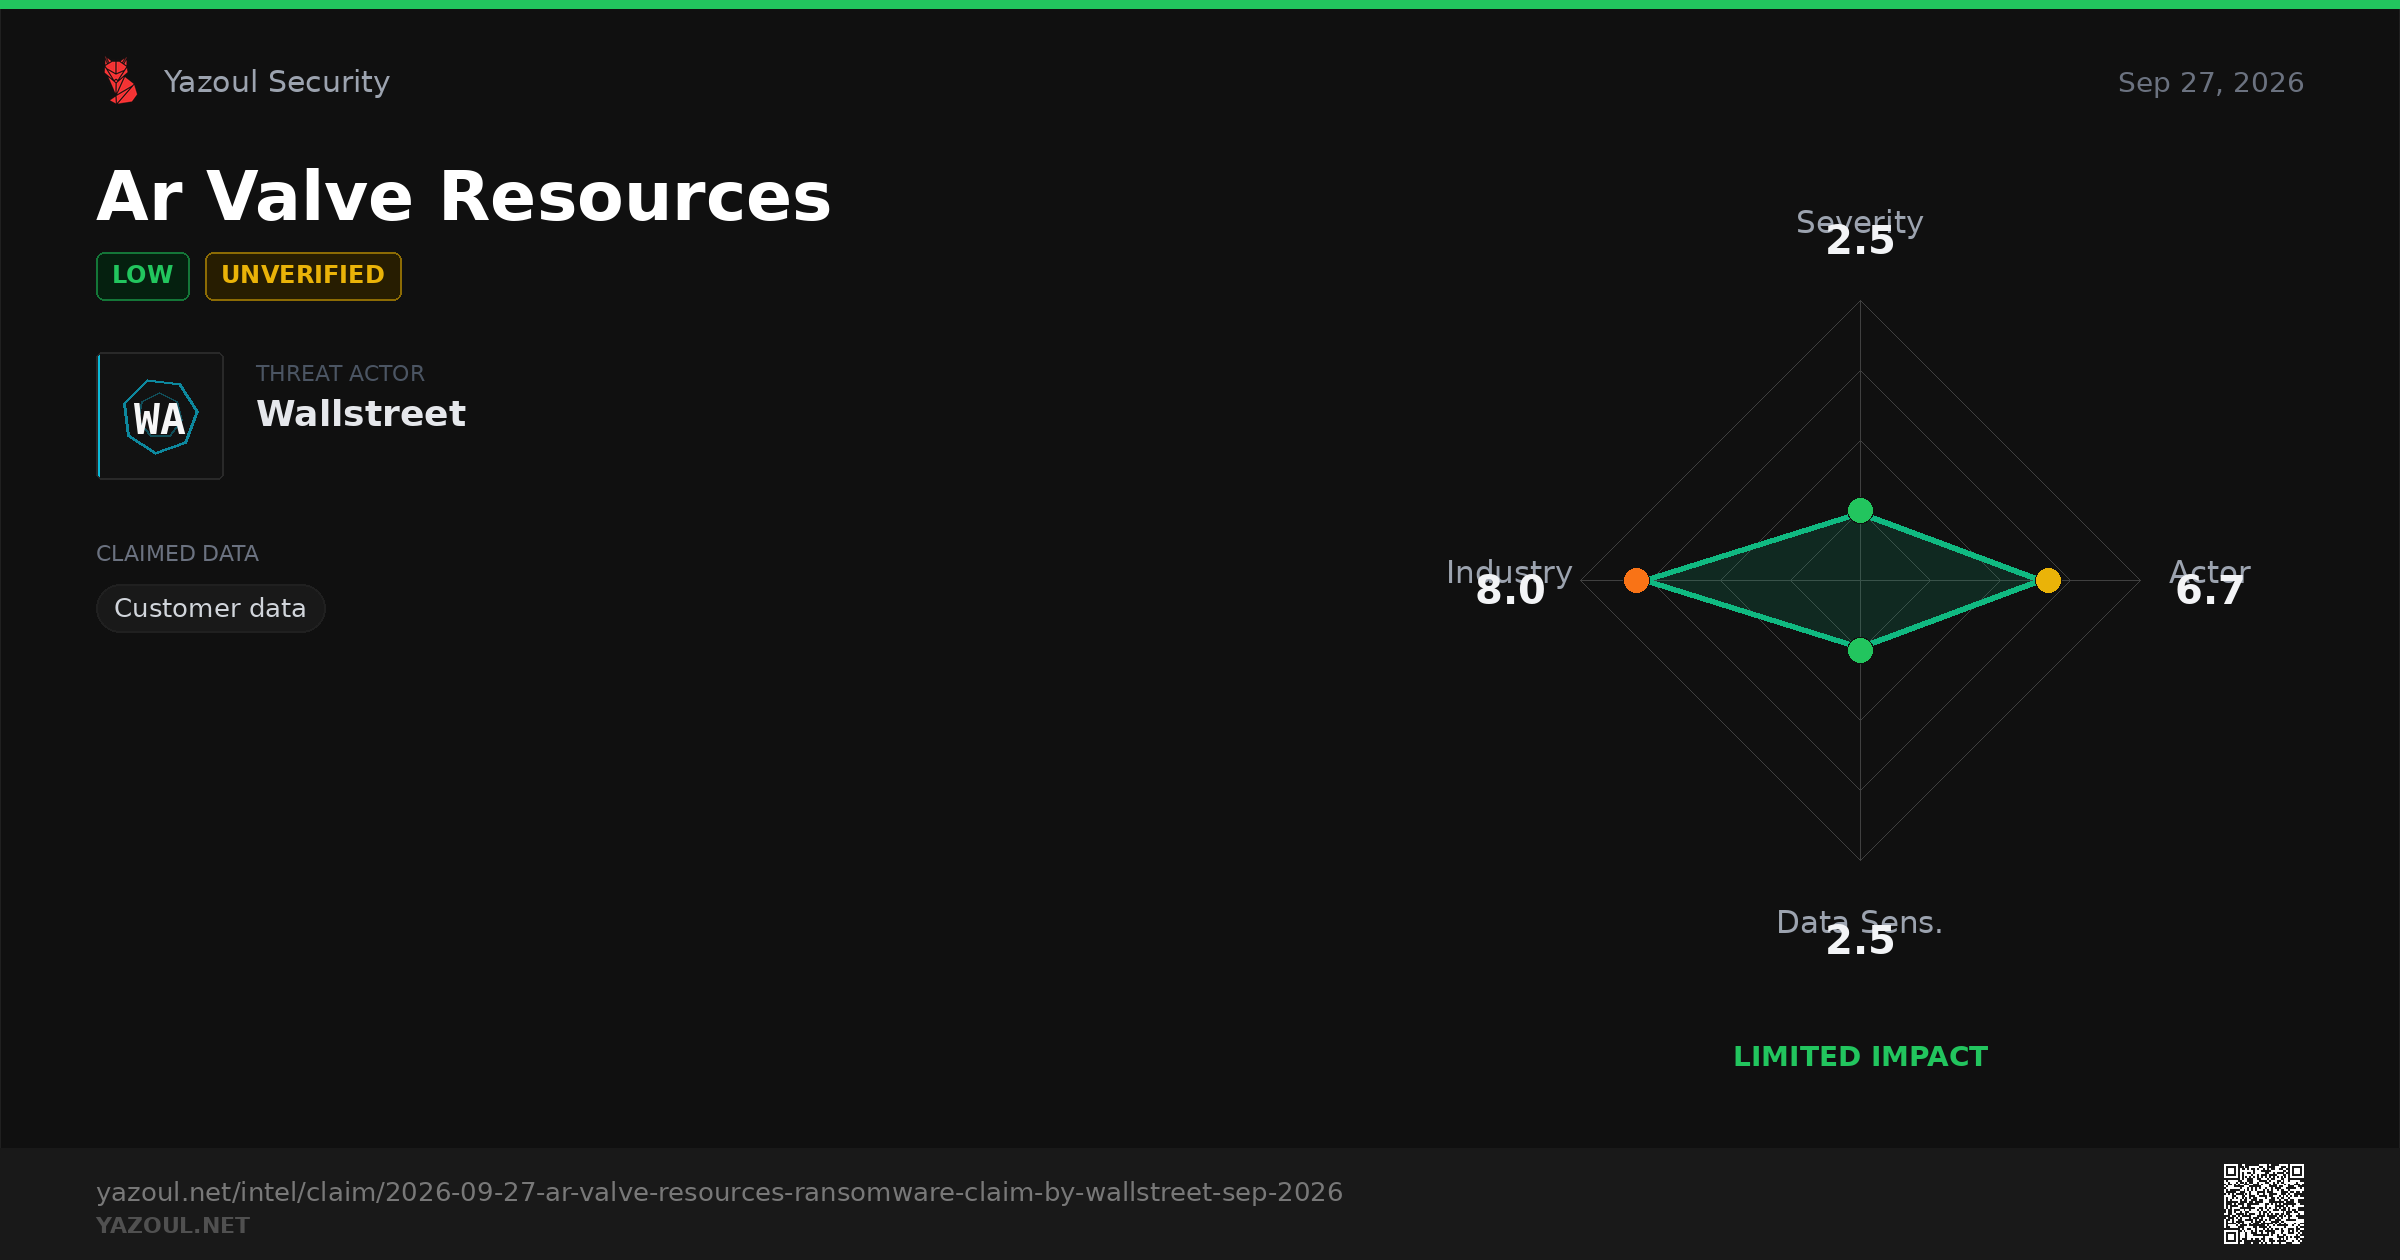
🛡 THREAT INTEL | Ar Valve Resources
🟢 Actor "Wallstreet" claims Undisclosed
Allegedly exposed
• Customer data
⚠️ Unverified claim
https://www.yazoul.net/intel/claim/2026-09-27-ar-valve-resources-ransomware-claim-by-wallstreet-sep-2026
by Yazoul AI
#DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
🤖 Bitget resumes BTC withdrawals after a $387.5M heist. Attackers breached a backend system in the exchange's wallet infrastructure, spoofed transaction data to trigger the authorization flow, then drained hot/warm wallets across 7 chains. DPRK-linked, per on-chain tracing.
🔗 https://www.bleepingcomputer.com/news/security/bitget-resumes-bitcoin-withdrawals-after-3875-million-crypto-heist/
#CyberSec #Crypto #ThreatIntel #InfoSec
Gambit reports a Chinese-speaking financially motivated actor using three open-source AI agents to automate vuln discovery and exploitation against online retailers. 105 projects between Sept 10-15 led to at least 27 compromises for payment-card theft. It shows low-cost AI scaling web-skimming operations. #AiAgents #RetailSecurity #ThreatIntel
🇧🇩 We tracked blacknet-00 claiming unauthorized access to Bangladesh Army network infrastructure at Qadirabad Cantonment. The actor alleges compromise of over 400 devices with access to PPPoE connections, backup files containing passwords, login logs, and router configurations. blacknet-00 has logged 19 incidents in the past week across our monitoring. #InitialAccess #ThreatIntel
This entry + more →
Compromised Ukrainian business sites are serving a fake Cloudflare CAPTCHA via hidden iframes. Clicking copies an msiexec command that victims are told to run via Windows Run, installing Psychedelic Stealer. Abuse of trusted sites and native binaries makes detection harder. #ClickFix #InfoStealer #Cloudflare #ThreatIntel
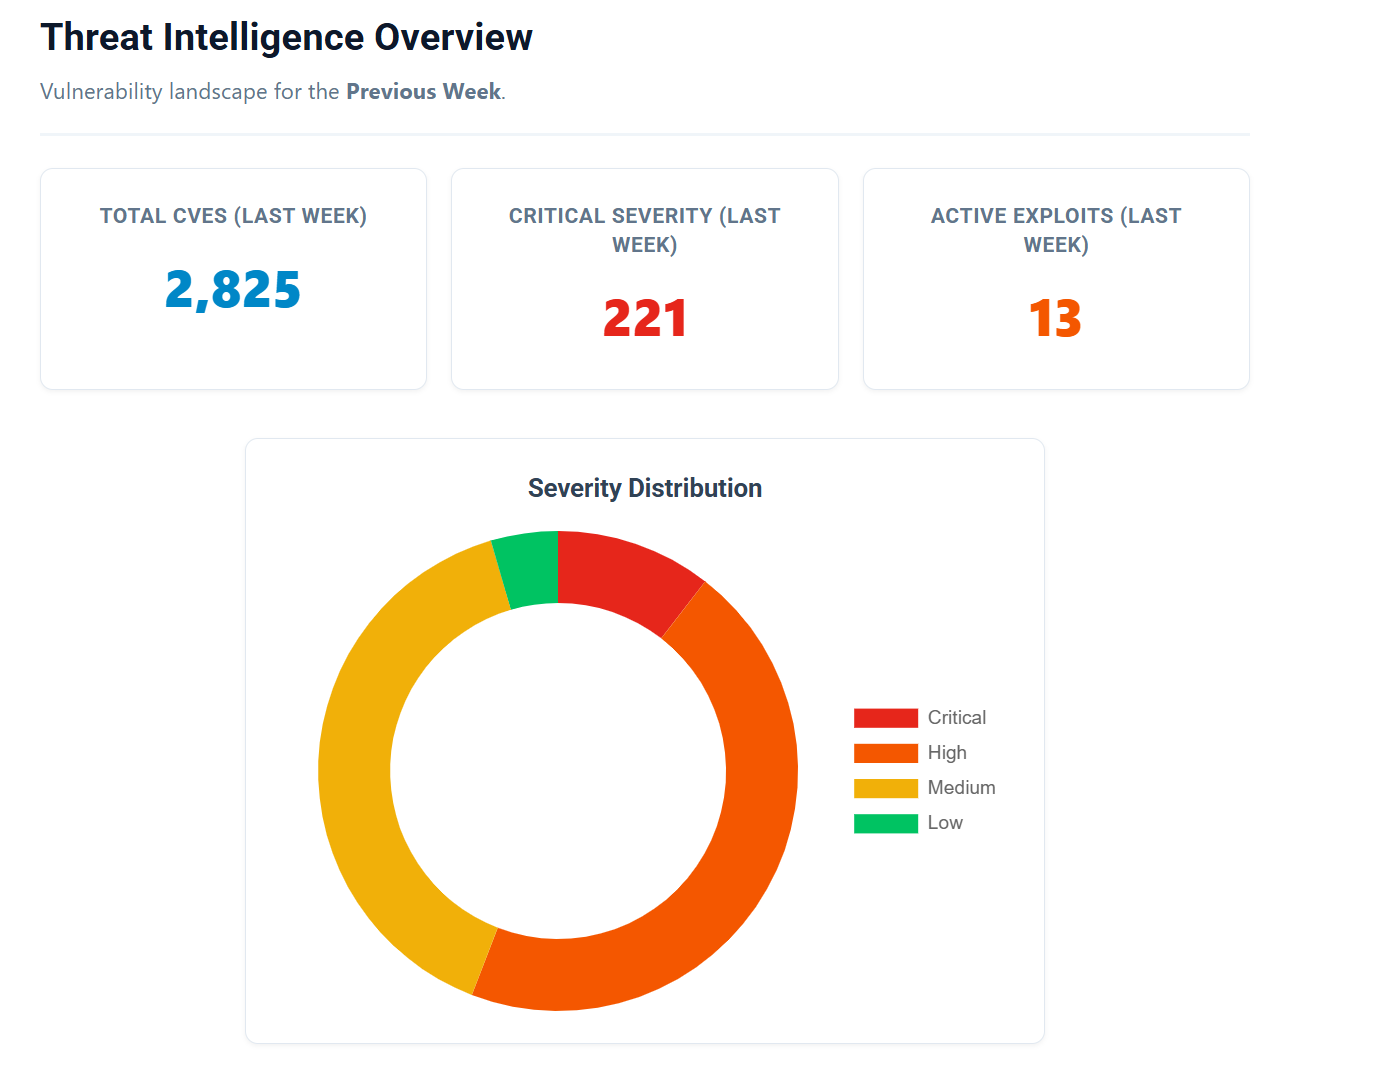
This weekly CVE report tracks 2,825 new flaws and 9 exploited vulnerabilities, verified against CISA KEV. WordPress, F5, Citrix and Check Point lead.
#WeeklyCVEReport #ExploitedVulnerabilities #CISAKEV #WordPressSecurity #CitrixNetScaler #F5BIGIP #CheckPoint #ThreatIntel
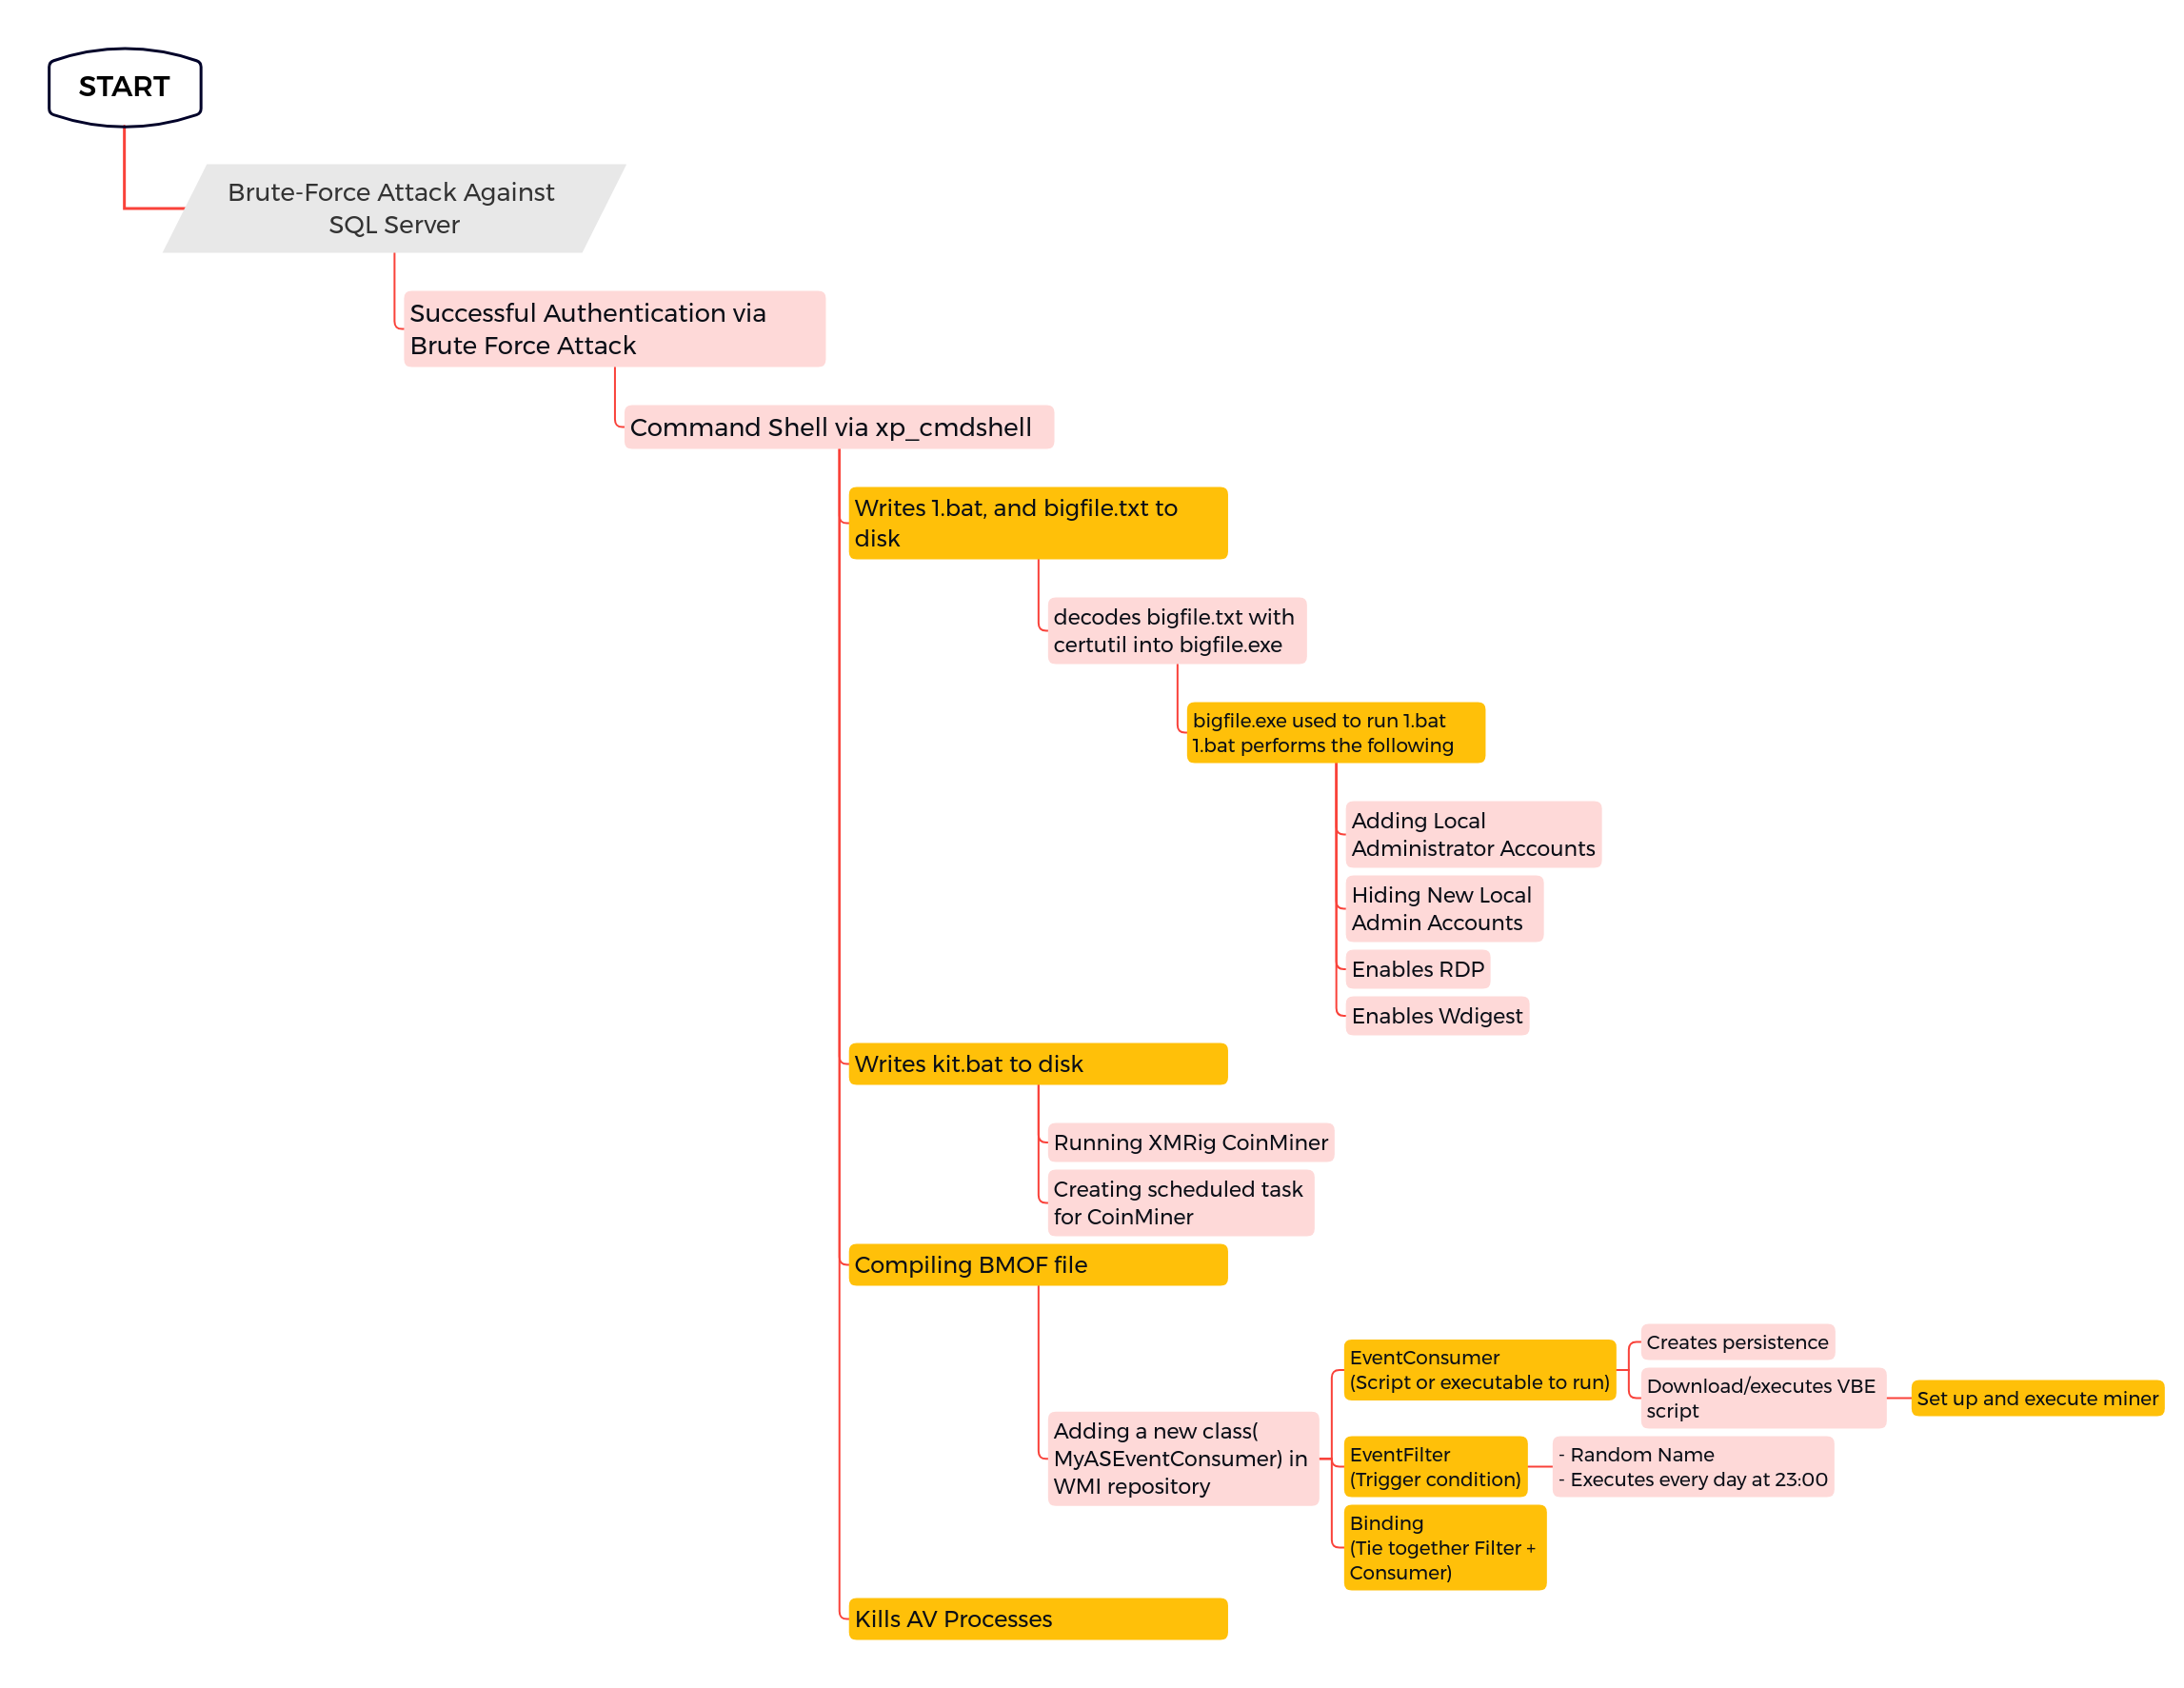
"The privilege escalation tool the threat actors brought with them was written as a text file and then decoded using certutil into a binary file."
Read the full report: https://thedfirreport.com/2022/07/11/select-xmrig-from-sqlserver
#DFIR #ThreatIntel
Google reports active exploitation of CVE-2026-35273 in Oracle PeopleSoft PeopleTools by UNC6240, linked to ShinyHunters. Encoded requests evade WAF rules to deploy JSP webshells via the Environment Management Hub, enabling persistent access. Prioritize patching and compromise hunting. #OracleSecurity #PeopleSoft #ThreatIntel
Boosted by @welcome@friends.deko.cloud
OffSeq is an European offensive security company.
We do pentesting, red teaming, OT/ICS and critical infrastructure security, and NIS2/DORA work across the EU.
Here we post our research: vulnerability disclosures (latest in Latvian and Estonian eID software and X-Road), monthly Mirage honeypot field reports and open-source tools.
Open to collaboration, DMs are open.
https://offseq.com/en/
#Introduction #InfoSec #PenTest #RedTeam #ThreatIntel #OffensiveSecurity