#apt

104 posts · Last used 6d

I managed to install a virtual machine of Debian with no SystemD! I mostly followed the instructions on the wiki, with the following modifications: 1) During the graphical installation, I selected no desktop (just standard system utilities and base system). I waited to install Plasma until after fixing the init system. 2) The wiki suggests running chroot /target. I tried it and got an error that no such directory exists. Instead, I ran chroot / . I would try changing this on the wiki but account registration is disabled. 3) When the wiki suggests installing apt --purge --allow-remove-essential install sysvinit-core libpam-elogind dbus-x11 systemd-sysv-, I also installed openrc at the same time. 4) apt gave a bunch of errors claiming it couldn't uninstall systemd. However, after rebooting, it used openrc to boot. I could then run # apt purge systemd followed by #apt-mark hold systemd without trouble. 5) Only after purging systemd and holding it from my system did I install Plasma, Konsole, and SDDM. Systemd started to AI-ify with version 260. Debian Trixie uses systemd 257, but Forky will probably use ≥260. My current plan is to stay with Debian until Forky rolls around, and then either a) Switch to Void b) Switch to Alpine, or c) Stay with Debian but replace systemd with openrc.
0
0
0
1
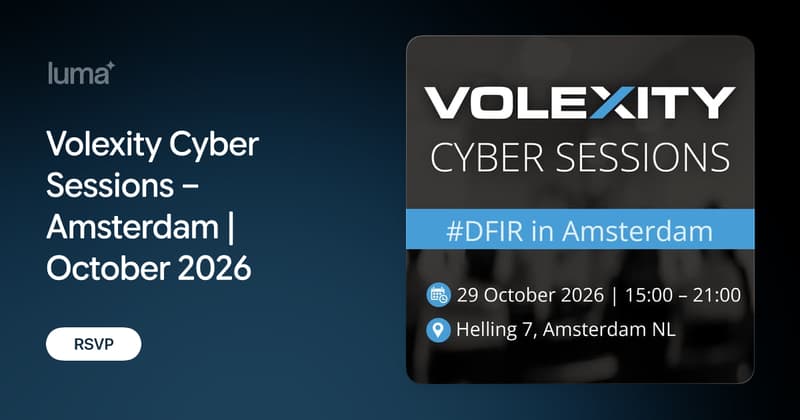
State-aligned threat actors continue to evolve their operations and infrastructure tactics. Feike Hacquebord will be speaking at our upcoming Volexity Cyber Sessions in Amsterdam (October 29) about APT campaigns by Russia-, China-, and DPRK-aligned actors targeting Europe in 2026. Feike will examine China-aligned residential proxy networks built on compromised IoT devices, DPRK-aligned operations run from static Russian IP addresses and hundreds of VPS servers, and a decade of Pawn Storm (APT28/Fancy Bear) activity. He will also explain how domestic Chinese AI capabilities have reduced China-aligned actors' dependence on frontier Western models. Seating is limited. Register now to secure your spot: https://luma.com/0qtkw49c #dfir #threatintel #apt
0
0
0
1
Replying to
Reward: You've received a laminated Storm-2570 Awareness Certificate. It does not stop ransomware. https://www.microsoft.com/en-us/security/blog/2026/09/24/beyond-ransomware-tracking-storm-2570-consistent-tradecraft-across-deployments #Ransomware #ThreatIntelligence #Storm2570 #CyberSecurity #APT #FollowTheTrail (3/3)
0
0
0
0
Replying to
Known issue: the group demonstrates rapid customization across multiple platforms simultaneously, which is a feature for them and a bug for you. Patch Google Chrome and Microsoft Windows immediately. Reward: You've received a Changelog of Regret. It ships with no hotfix. https://osintsights.com/china-aligned-group-exploits-chrome-microsoft-zero-days?utm_source=mastodon&utm_medium=social #ZeroDay #CyberSecurity #Chrome #Windows #APT #ExploitChainUnlocked (2/2)
0
0
0
0
Replying to
Reward: You've received a complimentary Pending Ticket — estimated resolution time is never. https://thehackernews.com/2026/09/china-linked-hackers-exploit-chrome.html #CyberSecurity #ZeroDay #Chrome #Windows #APT #Malware (3/3)
0
0
0
0
Alert. Masowo hackują sieci WiFi w hotelach / kawiarniach / na konferencjach na całym świecie. Cel: podróżujący pracownicy korporacji. O akcji ostrzega Microsoft, pisząc: zidentyfikowaliśmy w kilku krajach powszechne naruszenia bezpieczeństwa sieci WiFi w organizacjach z branży hotelarsko-gastronomicznej oraz w innych sieciach obsługiwanych przez urządzenia wspierające captive portal.Najpierw przejmowane są routerki dające dostęp do sieci WiFi. Umówmy się, często jedynym zabezpieczeniem w hotelu jest nieaktualizowany od 5 lat TP-Link... #Aktualności #Apt #Cyberawareness #Hotele #Rosja #Wifi
3
0
4
0
Replying to
Reward: You've received the Gilded Pitfall — a decorative tile that is also a pit. #AISecurityBreach #HuggingFace #CyberSecurity #ZeroDay #APT #AchievementUnlocked (3/3)
0
0
0
0