#fediadmin

78 posts · Last used 3d

Boosted by @fedicat@pc.cafe
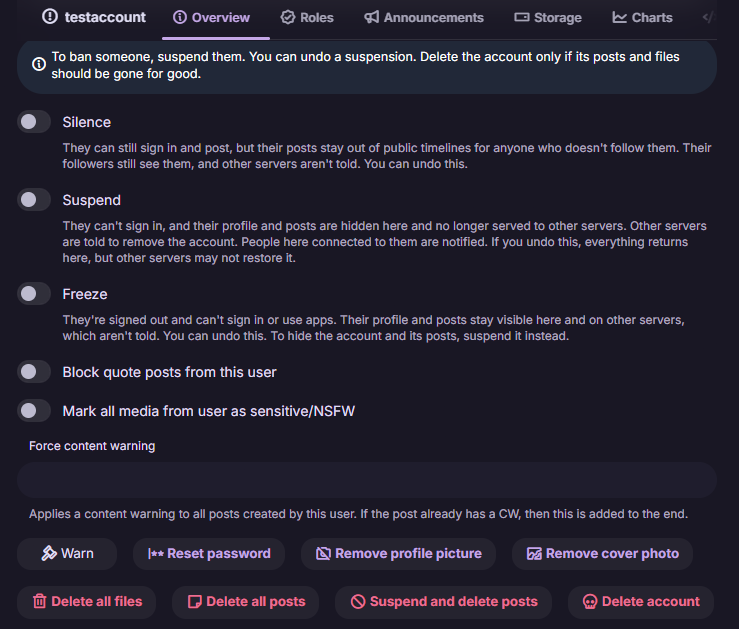
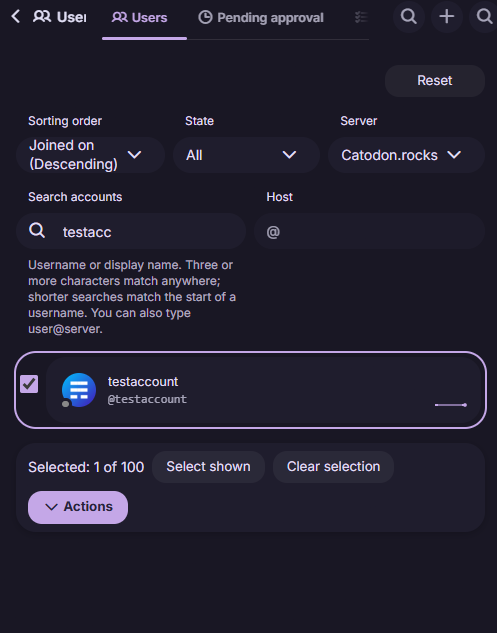
One of the things that have me seriously worried about AI lately is how easy it gets for bots to make Fediverse accounts - they can bypass bot protection guards at registration, as they can act more and more like humans. A mass influx of spambots could seriously bring servers to their knees and make the network unusable. So we need stronger moderation tools! Our next release will not only have more moderation options per user, but you will be able to apply them to up to 100 accounts at once. I really hope fedi admins won't need to deal with something like that, but it's always better to be prepared to defend your community. #catodon #misskey #sharkey #fediverse #fediAdmin RE: https://catodon.rocks/notes/at1yhevtndm501k9
Quoting
Improved moderation tools in the upcoming Catodon 26.11.0 "Nyan Cat" release Take a look at our enhanced moderation tools for Catodon admins - you can now also delete all posts by a user (plain Suspend just hides their posts locally, it doesn't federate a delete), and you can do mass moderation actions for up to 100 accounts at once! The RC for 26.11.0 "Nyan Cat" will be released in the next few days. ​:catodon:​ #catodon
Open quoted post
0
0
2
0
Mastodon admins! There is a spam wave hitting the Fediverse consisting of many mentions and a dubious/dangerous web link. You can find help for dealing with this at: ➡️ @iftas@mastodon.iftas.org IFTAS is posting and sharing lots of practical suggestions, and it is well worth following them anyway as they provide valuable resources for Fediverse safety. If you browse their timeline at @iftas@mastodon.iftas.org you'll see all their posts and shares. #MastoAdmin #FediAdmin #Spam
21
4
50
0
There are major account take-over problems happening right now on mastodon instances - all appearances are that the actor is using stolen passwords, probably from malware running on desktops. I've suspended hundreds of compromised accounts over the past 48 hours, but only two on mine. If you run a mastodon instance, here is a postgres query I use to randomize the passwords of accounts that have been inactive for 6 months or more. It also removes logged in sessions. This doesn't lock people out, just makes them perform a password reset. Yes, I wish I didn't have to do this, but here we are. I hope it helps someone else. BEGIN; CREATE TEMP TABLE dormant_batch ON COMMIT DROP AS SELECT u.id AS user_id FROM users u WHERE COALESCE(u.current_sign_in_at, u.created_at) < now() - interval '6 months' AND NOT u.otp_required_for_login AND NOT EXISTS (SELECT 1 FROM webauthn_credentials w WHERE w.user_id = u.id) AND NOT EXISTS (SELECT 1 FROM oauth_access_tokens t WHERE t.resource_owner_id = u.id AND t.revoked_at IS NULL AND t.last_used_at > now() - interval '6 months'); UPDATE users u SET encrypted_password = '$2a$10$' || left(replace(gen_random_uuid()::text || gen_random_uuid()::text, '-', ''), 53), updated_at = now() FROM dormant_batch b WHERE u.id = b.user_id; UPDATE oauth_access_tokens t SET revoked_at = now() FROM dormant_batch b WHERE t.resource_owner_id = b.user_id AND t.revoked_at IS NULL; DELETE FROM session_activations s USING dormant_batch b WHERE s.user_id = b.user_id; SELECT COALESCE(y::text, 'total') AS last_seen_year, count(*) AS locked FROM (SELECT date_part('year', COALESCE(u.current_sign_in_at, u.created_at))::int AS y FROM dormant_batch b JOIN users u ON u.id = b.user_id) s GROUP BY ROLLUP (y) ORDER BY y NULLS LAST; COMMIT; #mastoadmin #fediadmin
320
21
380
8

Because of the Social Media Platforms (Ofcom Licensing) Bill in the uk, fediverse admins globally now have to get a license to be able to be connectable from the uk.

Edit: I forgot to add that this hasn't passed yet, but it probably will because politicians don't listen to us here

This is the bill: https://bills.parliament.uk/bills/4285

Please not that it says operating in the uk not operating from the uk, so it applies globally.

To get a license:

  • You have to send snail mail to ofcom to get a license
  • Employ a compliance team
  • Keep all your logs
  • Ensure that content made available does not "incite criminal conduct, violence, hatred or public disorder." Whatever the fuck that means, it's so vague you can make that anything
  • Ensure that content made available does not violate the laws of the uk... So you have to follow uk law outside of the uk now
  • Ensure that there isn't misinformation, so I would just not have to post misinformation on my lemmy instance then? Or is that not enough for them? I can't remove stuff on other instances you fucking morons
  • You have to dox all your users

The punishment for breaking any of these rules is as follows:

  • An unlimited fine
  • Up to two years of jail time
  • A court order to have ISPs block you(fucking horrible my lemmy instance is in my wardrobe I don't want my internet cut off)
  • And anything else the court " considers appropriate." Which is anything so just anything else

#fediadmin #fediverse #fuckwestminster #uk #authoritarianism #censorship #ofcom

35
8
46
0
Replying to
Wann bekommt @Mastodon@mastodon.social eigentlich vernünftige Hooks, damit man derlei besser erkennen und unterbinden kann? Macht hier den Mammutanteil aller Spam-Reports aus und im Mod-Interface kann man nichtmals erkennen, dass es Followspam ist, man sieht nur, dass ein Account reported wurde. Das ist völlig unzureichend, zumal es sich recht gut technisch erkennen ließe. #fediadmin
4
1
1
0
Salut tout le monde ! Je prépare une page d'acceuil pour notre serveur. J'aimerais bien inclure quelques pages qui ont des tips pour le fediverse, idéalement francophone. Des pages qui expliquent comment bien utiliser mastodon, comment ça marche sur le fediverse, comment trouver des comptes qui pourrait plaire ou toute autre information que vous auriez aimé avoir au début ! Je suis preneur de toute information, piste, etc ! 😃 Merciiiii ! #fediverse #mastodon #introduction #feditips #fediadmin
7
0
9
0
pix.lgbt has been moved off of pixelfed-glitch because development there has come to a hault and we are back to vanilla Pixelfed. We now have the latest and greatest version that released this morning (plus quite a few fixes we submitted upstream for the rest of the community 🤞). We hope you enjoy! Moving back was a bit of a PITA so there was some small hiccups along the way (sorry about that!) but everything should be good going forward! If you have any issues don't hesitate to reach out! And if you're not already here and looking for a new home for your photos on the fediverse our registration is open! Tell your friends! #PixelfedAdmin #FediAdmin #Pixelfed #RegistrationsOpen
0
1
1
0
⚠️ Mastodon 4.4.x ⚠️ You're being urged to upgrade to Mastodon 4.6.x for a reason. Mastodon plans to release v5 by the end of this year or early next. That's why we've jumped from 4.5 to 4.6, and now we're on 4.7, with 4.8 already in nightly builds. Certain features and functionalities will leave you behind, and 4.4.x will soon reach its end of life (EOL). If you're using Mastodon 4.4.x, you should aim for 4.6.x or newer. #Mastodon #MastoAdmin #FediAdmin
3
1
2
0
I'm going to preface this with that I have no intention of doing this at all, this is just a hypothetical that has been nagging me. Let's say I were to delete this instance tomorrow, or maybe the domain expires and I never renew it... Does the cache of my posts and info and such eventually disappear from other fediverse instances? Do posts have a TTL that gets refreshed with the originating server or anything like that? I am sure that it is different across different implementations, so I'm really just looking for a general answer... #fediadmin #fedi #activitypub
0
1
0
0
apparently this flood of "automated protocol delivery probe" spam signups comes from https://sendflood.com if we mass report them to their registrar's abuse thing they should stop spamming us? the site was only made like a week ago sources for this info: • https://wubba.boo/notes/ar9jffw36cmi1qh2 • https://bardicperspiration.club/@Overgoddess/117288027775455205 • https://fosspri.de/@joshix/117286960234031491 as per the attached image their registrar's abuse email is abuse@spaceship.com and abuse phone number is +1.9854014545 #FediAdmin #MastoAdmin #fediblock #spam
18
8
28
2
Boosted by @fedicat@pc.cafe
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet. On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave. Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything. The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth. So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client. If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include: location = /api/v1/accounts { limit_except GET { deny all; } try_files $uri @proxy; } This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes. #Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
67
10
65
4

If the answer to all these is yes, please DM me at @FediGarden@social.growyourown.services and tell me a bit about your server 🙂

#Fediverse #FediAdmin #MastoAdmin

46
2
73
0