#php
376 posts · Last used 1d
Observations from Running stealmybitcoin.com via @wezm@mastodon.decentralised.social https://lobste.rs/s/fgucra #php #security
https://pavursec.com/blog/stealmybitcoin/
Boosted by @trending@homestead.social
Boosted by @gvenema@fairmove.net
Even schaamteloos eigen werk promoten (voel je vooral niet verplicht te klikken). Ik heb na de #PHP-ellende van vorige week voor @NRC@nrc.social een verhaal gemaakt over #OpenSource en de financiering daarvan. Drie keer raden waar het lukte om contact te leggen met de hoofdpersoon @edorian@phpc.social. Dank ook aan @ronnylam@mastodon.social en @Brenno@mastodon.social https://www.nrc.nl/nieuws/2026/10/29/opeens-moest-de-slecht-gefinancieerde-stichting-achter-programmeertaal-php-keihard-aan-de-bak-a4939870 @wlaatje@social.edu.nl
Steal my #Bitcoin
There is a bitcoin key hidden on this server worth about $2,014.
It is accessible to the PHP user account through the print-flag binary.
This #PHP version was selected from before the #PHP2SHELL CVEs were released.
https://stealmybitcoin.com/
EDIT: Just wanted to clarify that this is not my initiative and I’m not affiliated with it. Sorry if my original post suggested otherwise, it was a quick copy/paste from the website (which seems to be down since several hours, by the way). I simply saw the link and I liked the idea.
Boosted by @dansup@mastodon.social
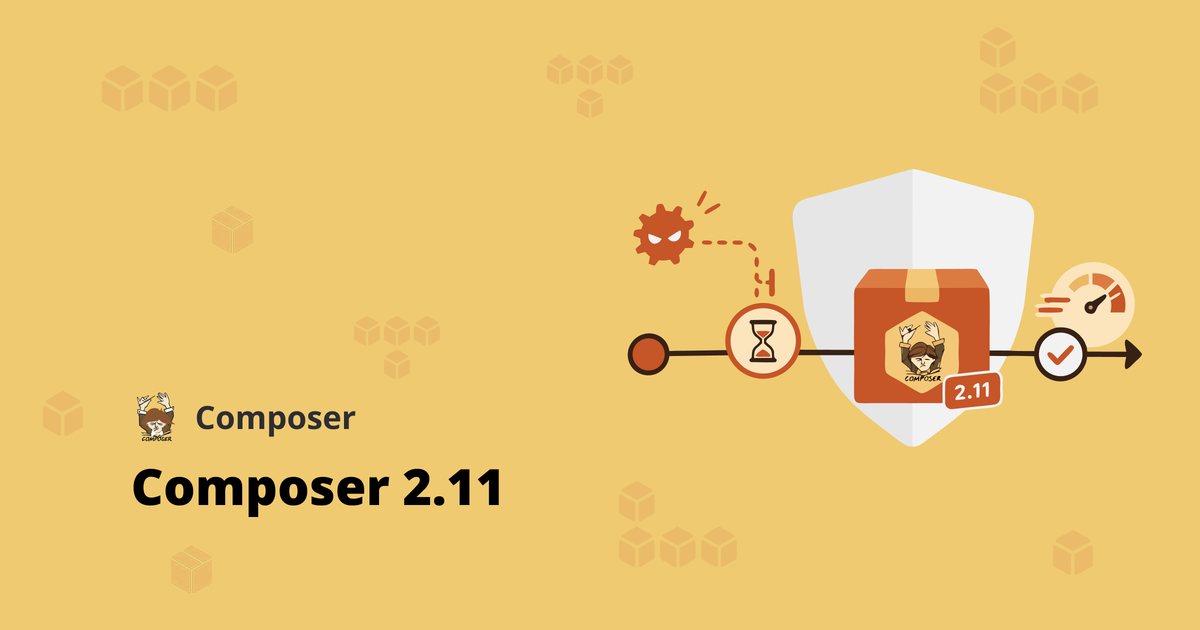
Composer 2.11 is out 🚀 cooldown dependency policies hold back freshly published package versions for an hour or a day, so compromised releases can be flagged before they reach your composer update.
Composer 2.11 includes several security fixes, block-scope support for custom dependency policies, OSC 7501 terminal progress reporting and faster and more memory efficient dependency resolution.
Full blog post: https://blog.packagist.com/composer-2-11-release/
#php #phpc #composerphp #supplychainsecurity
There isn't an easy exploit for this PHP vulnerability
I came across the link via https://mastodon.social/@CuratedHackerNews/117481600704689796
Last time I touched php it was ~20 years ago and maybe for a month. Could someone with actual php understanding weigh in?
Somehow, somewhere between the lines, my understanding was that there have been observances of the vuln being used in the wild before the 14 UTC. And that wasn’t from reading news sites
Reuters: “PHP Foundation under-funded” https://archive.is/iRxVy
If you use PHP or one of the many products that do ( #WordPress, #Drupal, #Joomla, #Laravel, #Symfony) please support @thephpf@phpc.social with a recurring donation.
https://thephp.foundation
#PHP
Boosted by @dansup@mastodon.social
Replying to
None of my posts on Bluesky ever get shared much. If you’re there, I’d appreciate a boost, please. 🙏
https://bsky.app/profile/ramsey.dev/post/3myx25vdrsrq2
#PHP
Boosted by @welcome@friends.deko.cloud
Hi Fediverse 👋 I'm Kevin, a PHP/Symfony developer and team lead from Germany.
Lately one question keeps me busy: how do you let AI coding agents write PHP without lowering the bar? My answer so far: quality gates first. PHPStan at max, Rector, ECS, tests, architecture rules, Infection.
I write about it at https://blog.tony-stark.xyz and share my templates on GitHub. Happy to swap notes!
#introduction #PHP #Symfony #PHPStan
@possible@masts.lv is recommending
the following temporary mitigation for the #PHP vulnerabilities about to be (or already being) actively exploited:
Boosted by @trending@homestead.social
Set session.upload_progress.enabled=0 until the next PHP release to block an unlikely RCE vector (CVE-2026-115560).
We already recommended this for CVE-2026-109619 from Wednesday: keep it disabled.
Only applications with non-default serialize_handler switching it to php at runtime can be affected.
There is more information in the advisory on the PHP website by the PHP security team: https://www.php.net/archive/2026.php#2026-10-23-1
(1/5) Some thoughts on yesterday's #PHP #vulnerability
🔒 Normally, vulnerabilities are patched before we hear about them, with key distributors notified in advance to reduce risk. This time, a security researcher accidentally published details early, and a for-profit PHP distributor broke embargo and leaked the fix. The vulnerability was exploited in the wild within the hour, making everything worse.
Replying to
Bonus thought: This comment on the #PHP blog alleges that Chainguard, the organisation who broke embargo and leaked the patch early, is currently using this to try to expand their customer base.
If these allegations are true, it's difficult to say how #Chainguard should still be allowed access to pre-disclosure information. If this happens again, the whole responsible disclosure system is at risk of collapse.
For some reason, a few of my clients’ e-commerce sites break after updating PHP. I can’t share any more details at the moment, as they’re still working on it.
On a completely unrelated note, two customers of my clients insisted on having a call, both involving the cybersecurity department of the massive corporate group they belong to. Wasted time… but ok.
One thanked us for responding so quickly. The other asked why their server hadn’t already been secured.
I explained that I had already applied the mitigations and installed the patch just ten minutes after it became available.
Their response: “You need to review your processes, because servers must be patched before the vulnerability is publicly disclosed.”
I ended the call laughing while eating a plate of tortellini.
#php #IT
Boosted by @dansup@mastodon.social
If all the governments shutting down their servers for a PHP vulnerability, all the hosting companies and enterprises terrified by the vuln, would give $100k, heck only $50k a year to the PHP Foundation, things could look very differently. Go make your employer sponsor *today* https://thephp.foundation/sponsor/ #php #phpc @thephpf@phpc.social
Now that we have finally found the main culprit for the breaking web (Of course it's PHP! It's long dead anyhow!) perhaps we can finally stop wasting time with fingerpointing and instead start fixing the real problems!
#php
Affected by PHP2Shell (CVE-2026-109618/CVE-2026-109619)? Freexian’s PHP LTS provides updates for PHP 5.6 and later on Debian 9+ and Ubuntu 18.04+. Explore our plans at https://www.freexian.com/lts/php/?utm_source=mastodon&utm_medium=social or get in touch to discuss your options.
#php2shell #php #freexian